
Articles
Asset and service inventory: knowing what you actually run
An inventory is a record with checkable properties, not a database: what CM-8 requires.
An inventory is a record with checkable properties, not a database: what CM-8 requires.
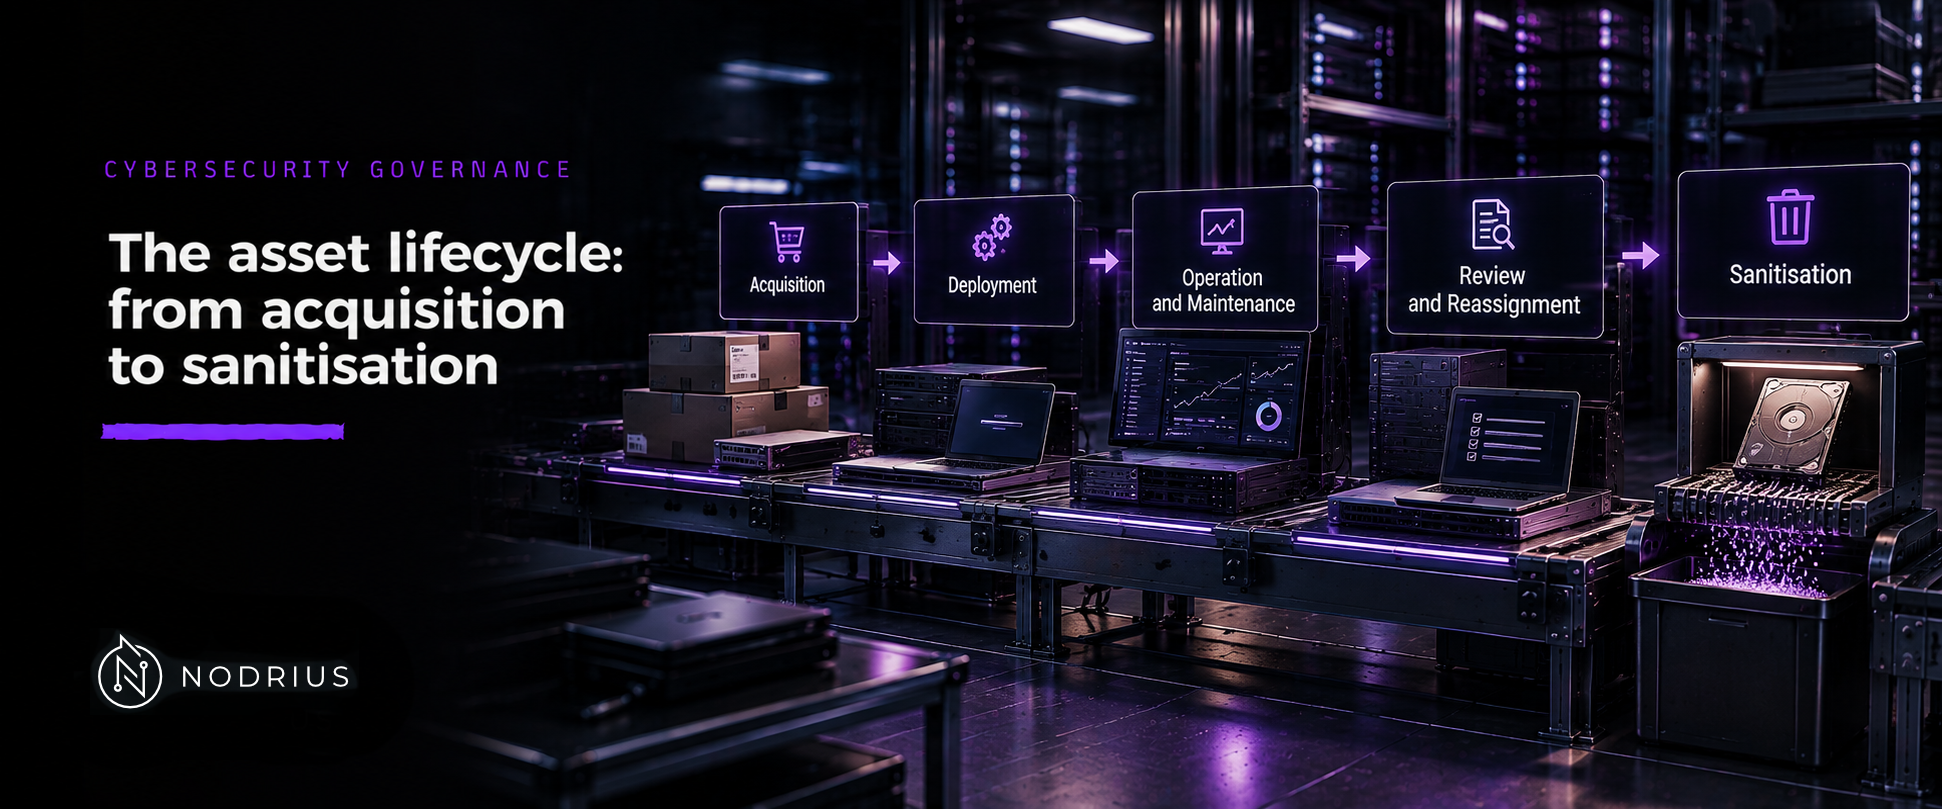
The inventory is a snapshot; the lifecycle is the process that ends an asset.
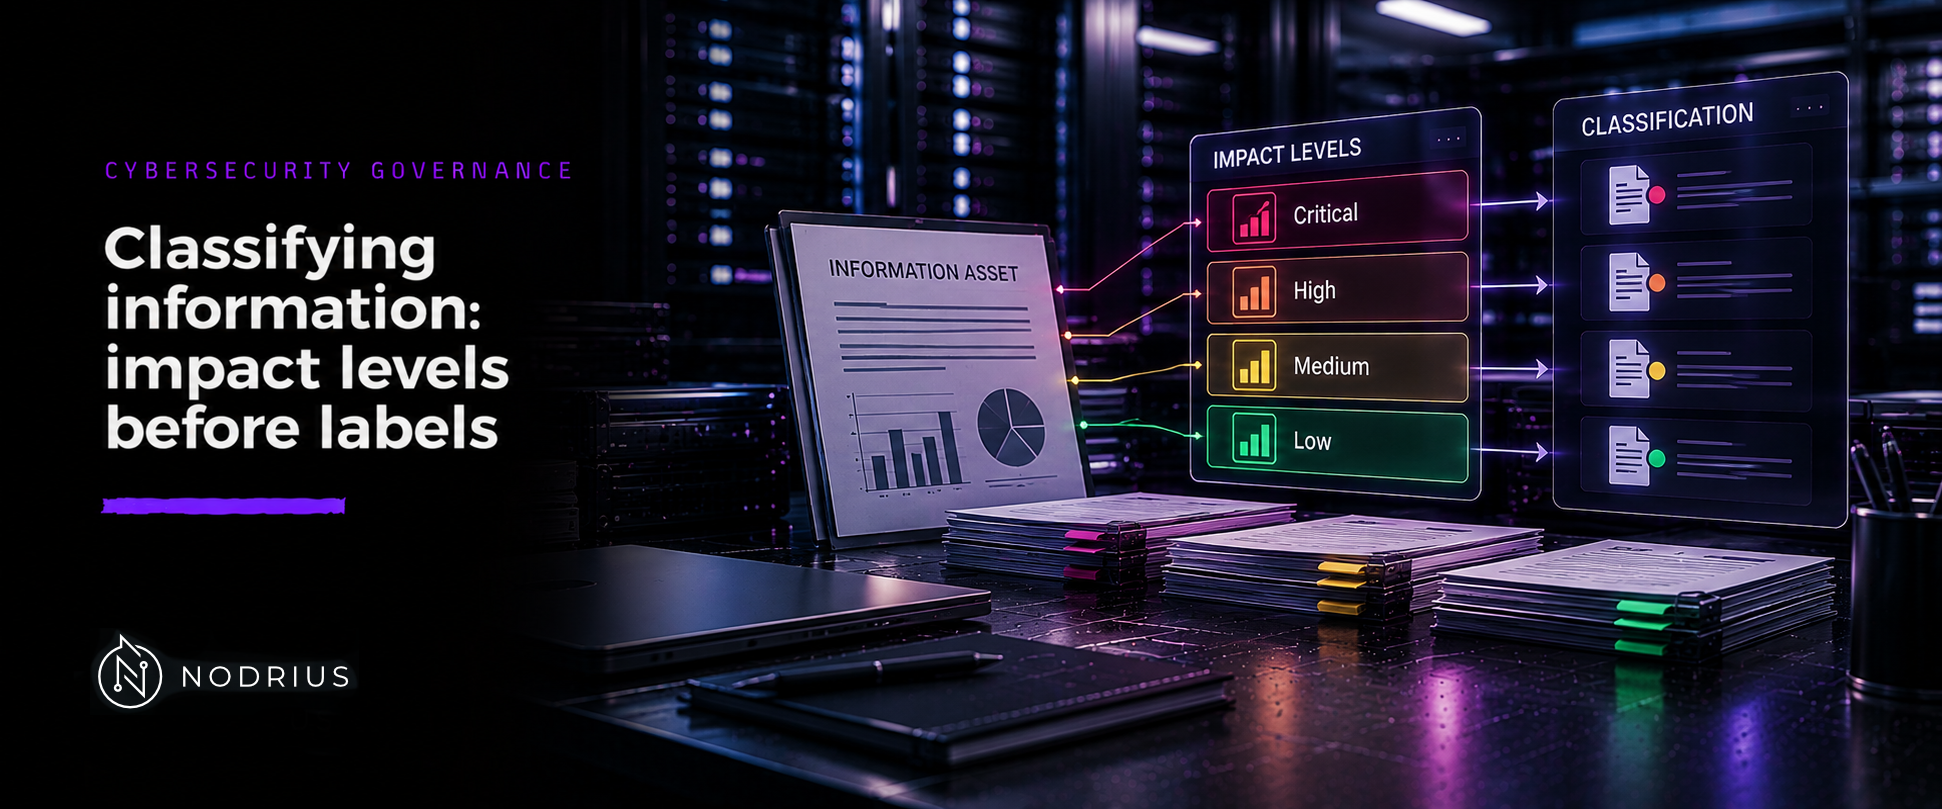
The impact level is the decision; the label only carries it to the object it governs.
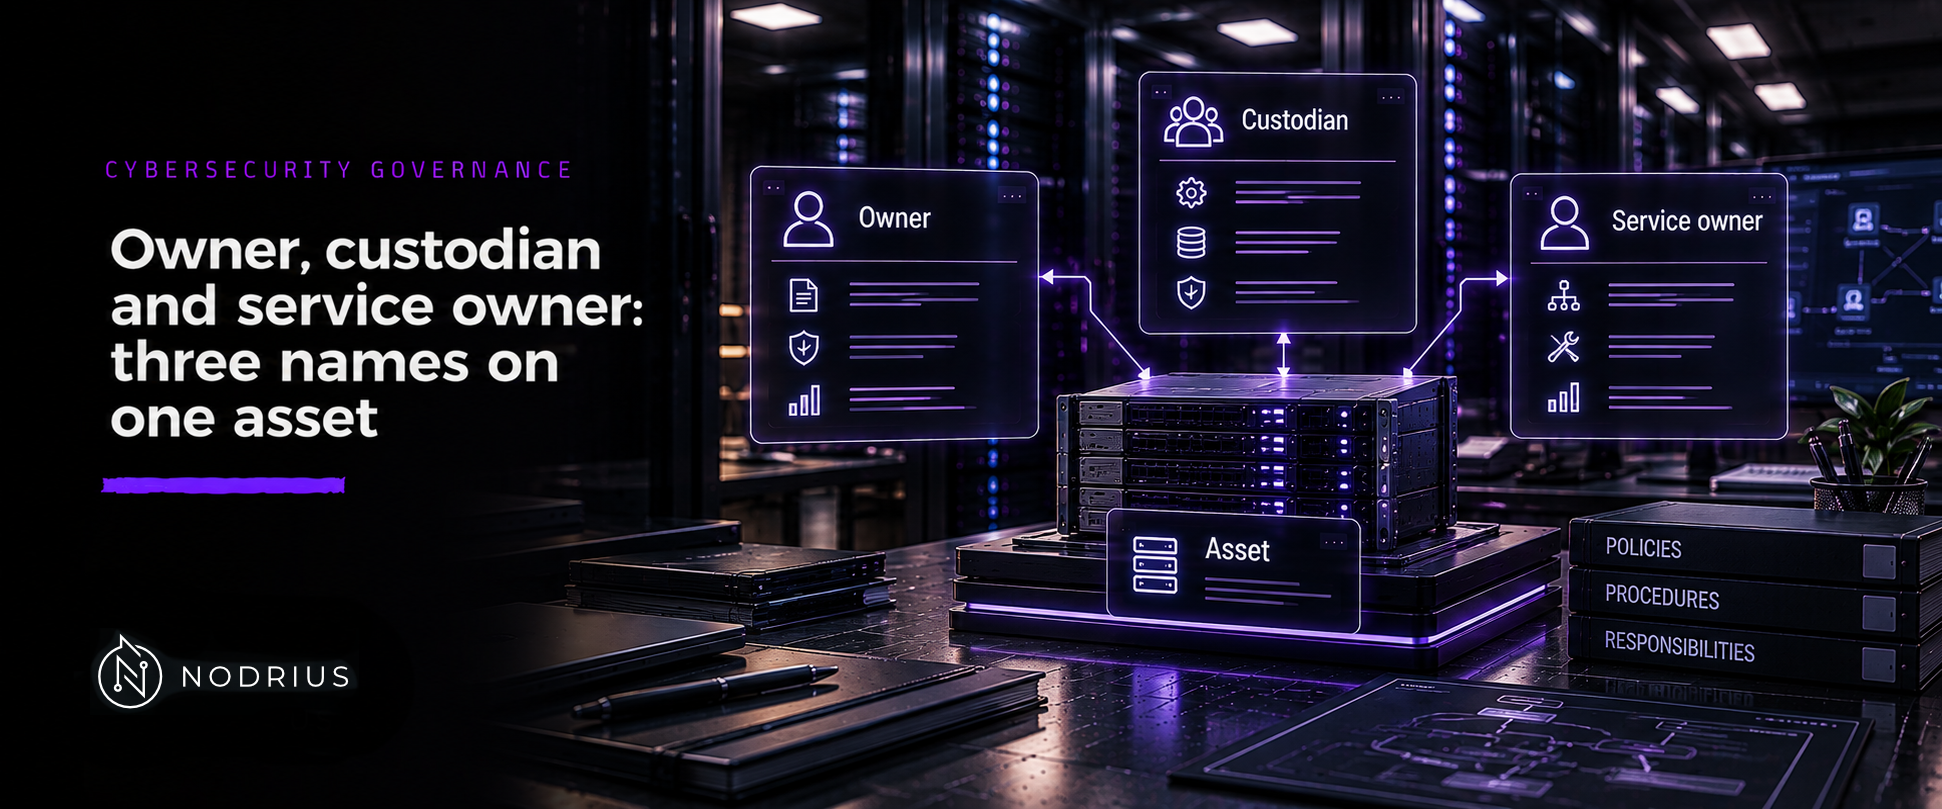
Three hats on one asset: who sets the rules, who runs it, and what the register names.
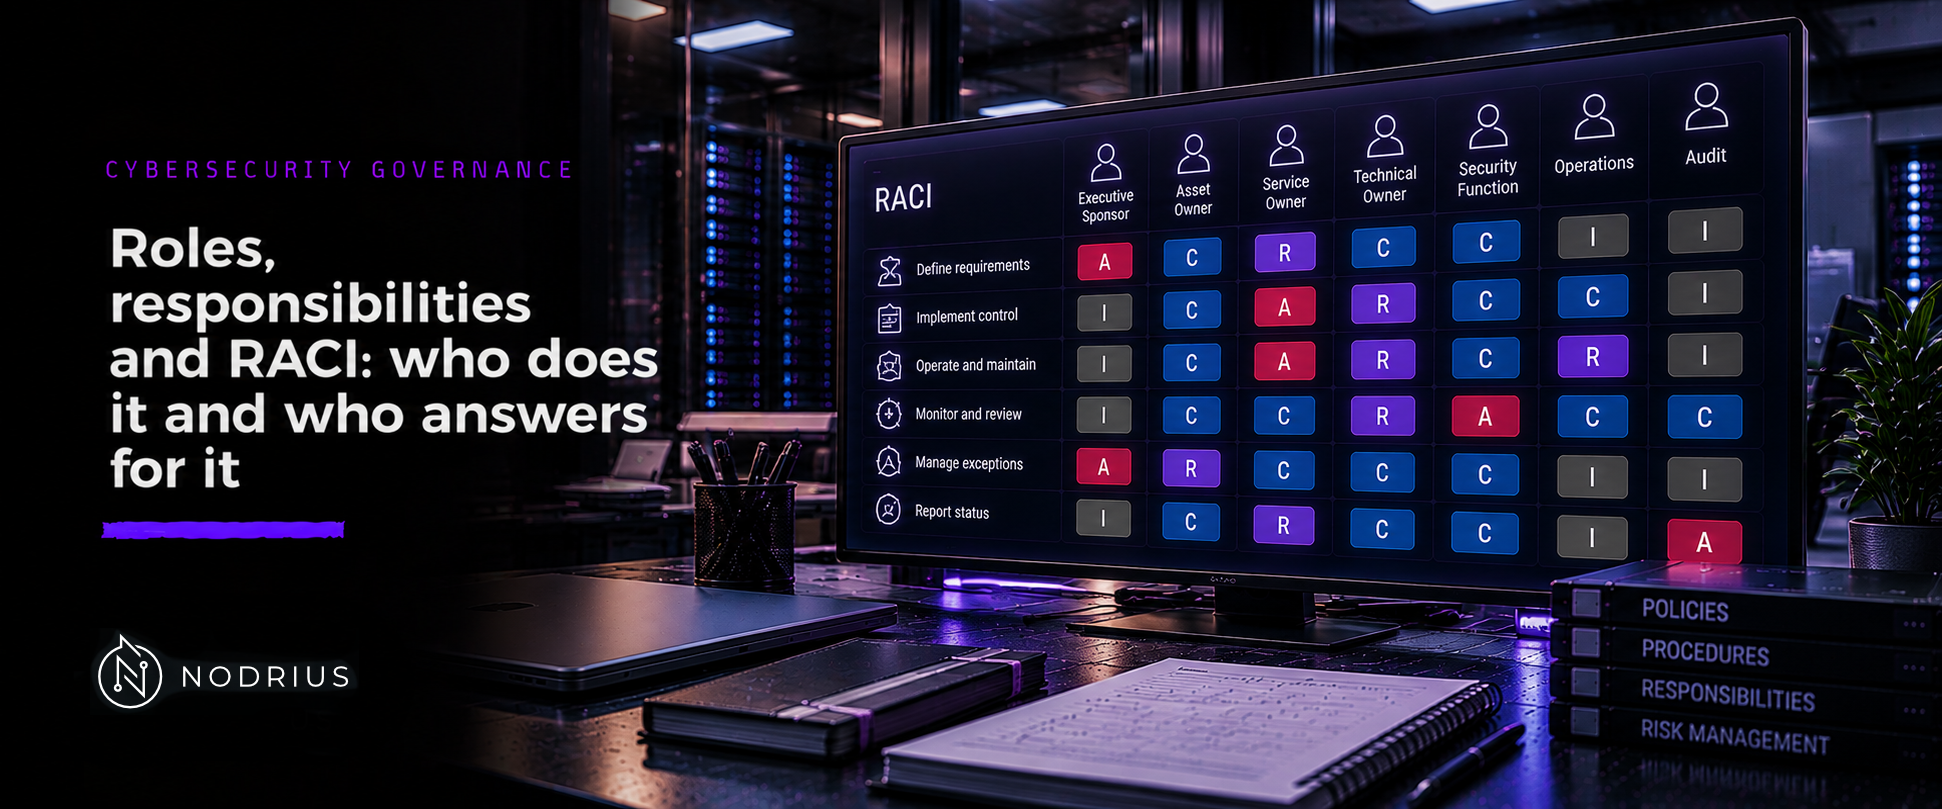
A RACI chart maps activities to roles; done badly it hides who answers for what.
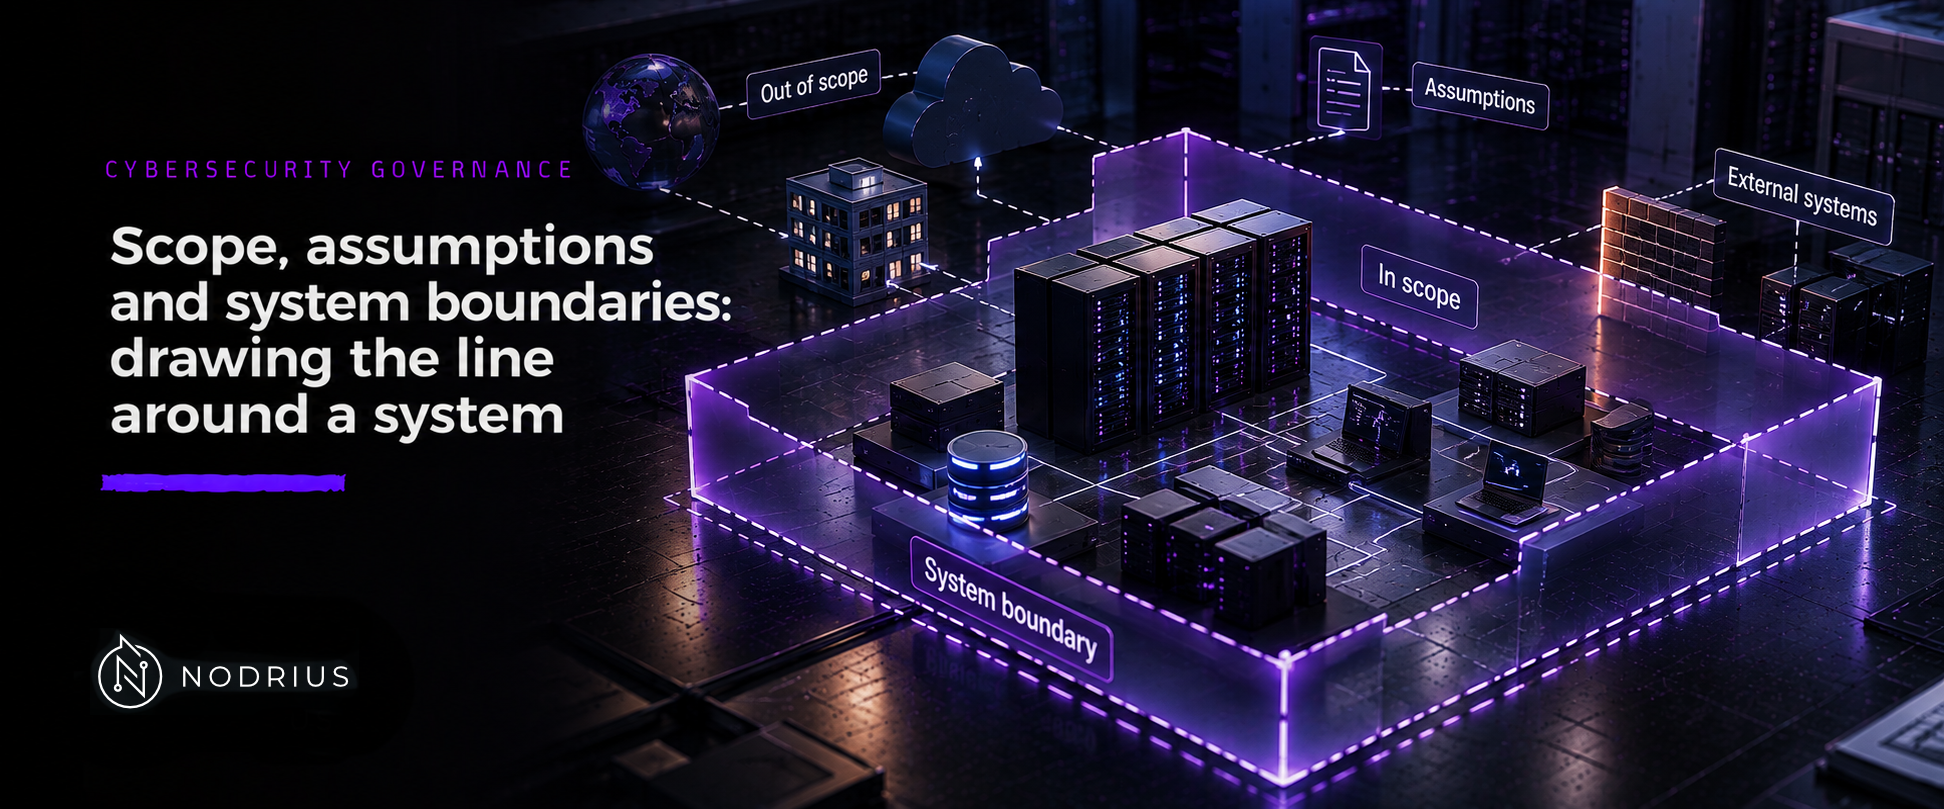
Drawing a system boundary: the decision it encodes and the assumptions it rests on.
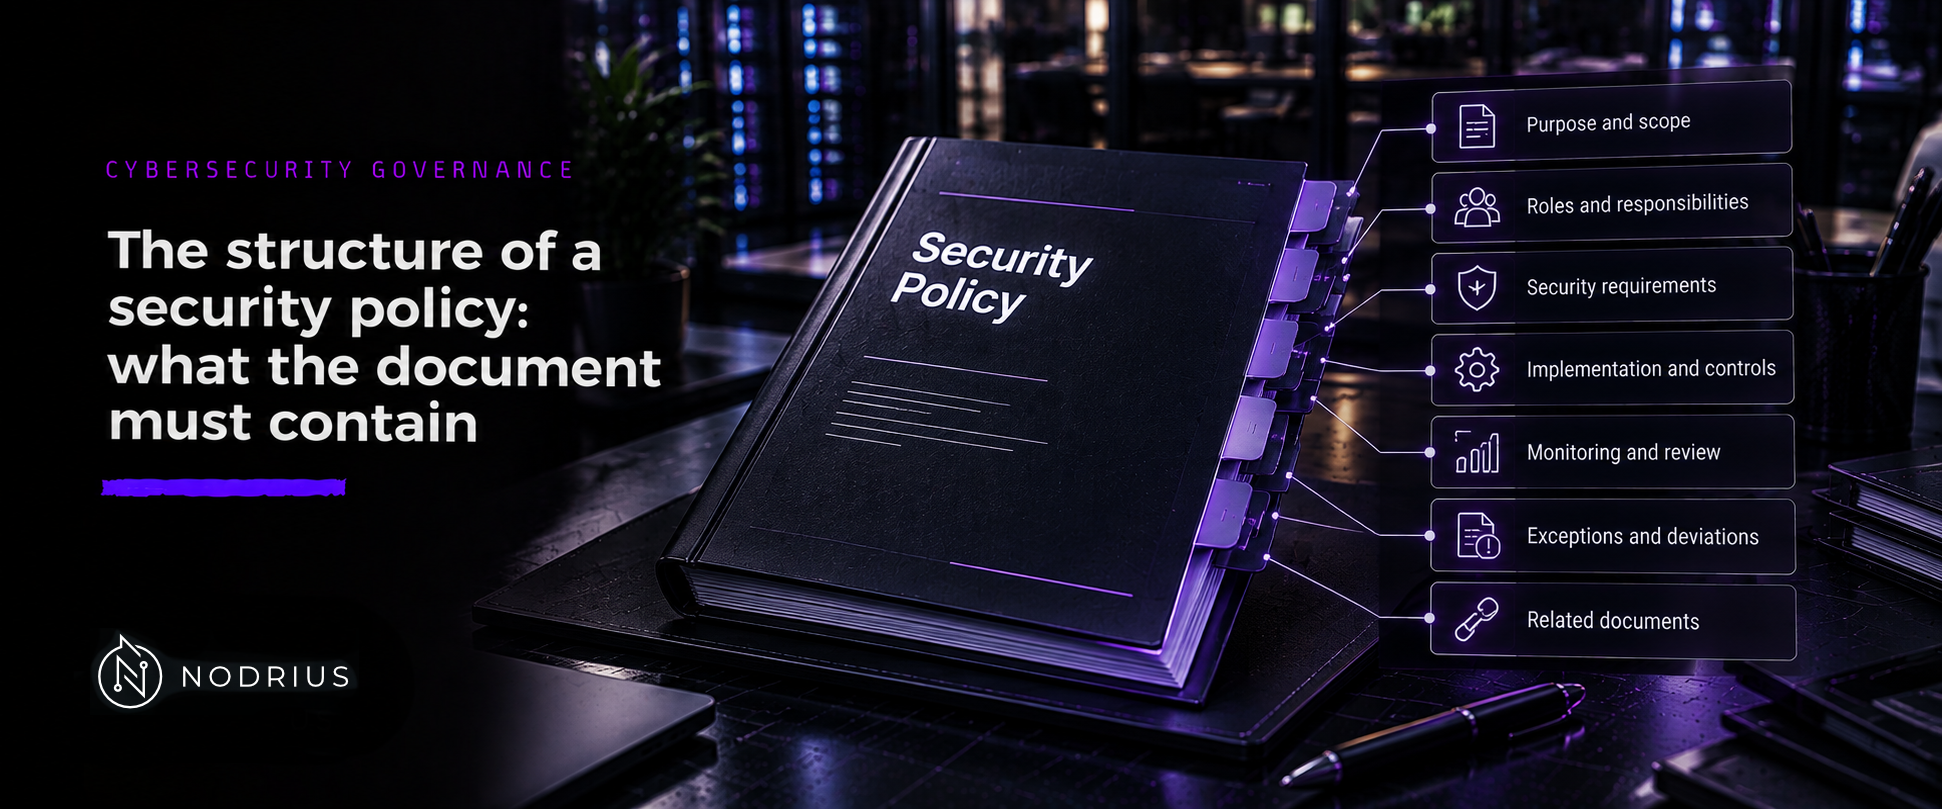
The parts a security policy must contain, and what their presence does not prove.
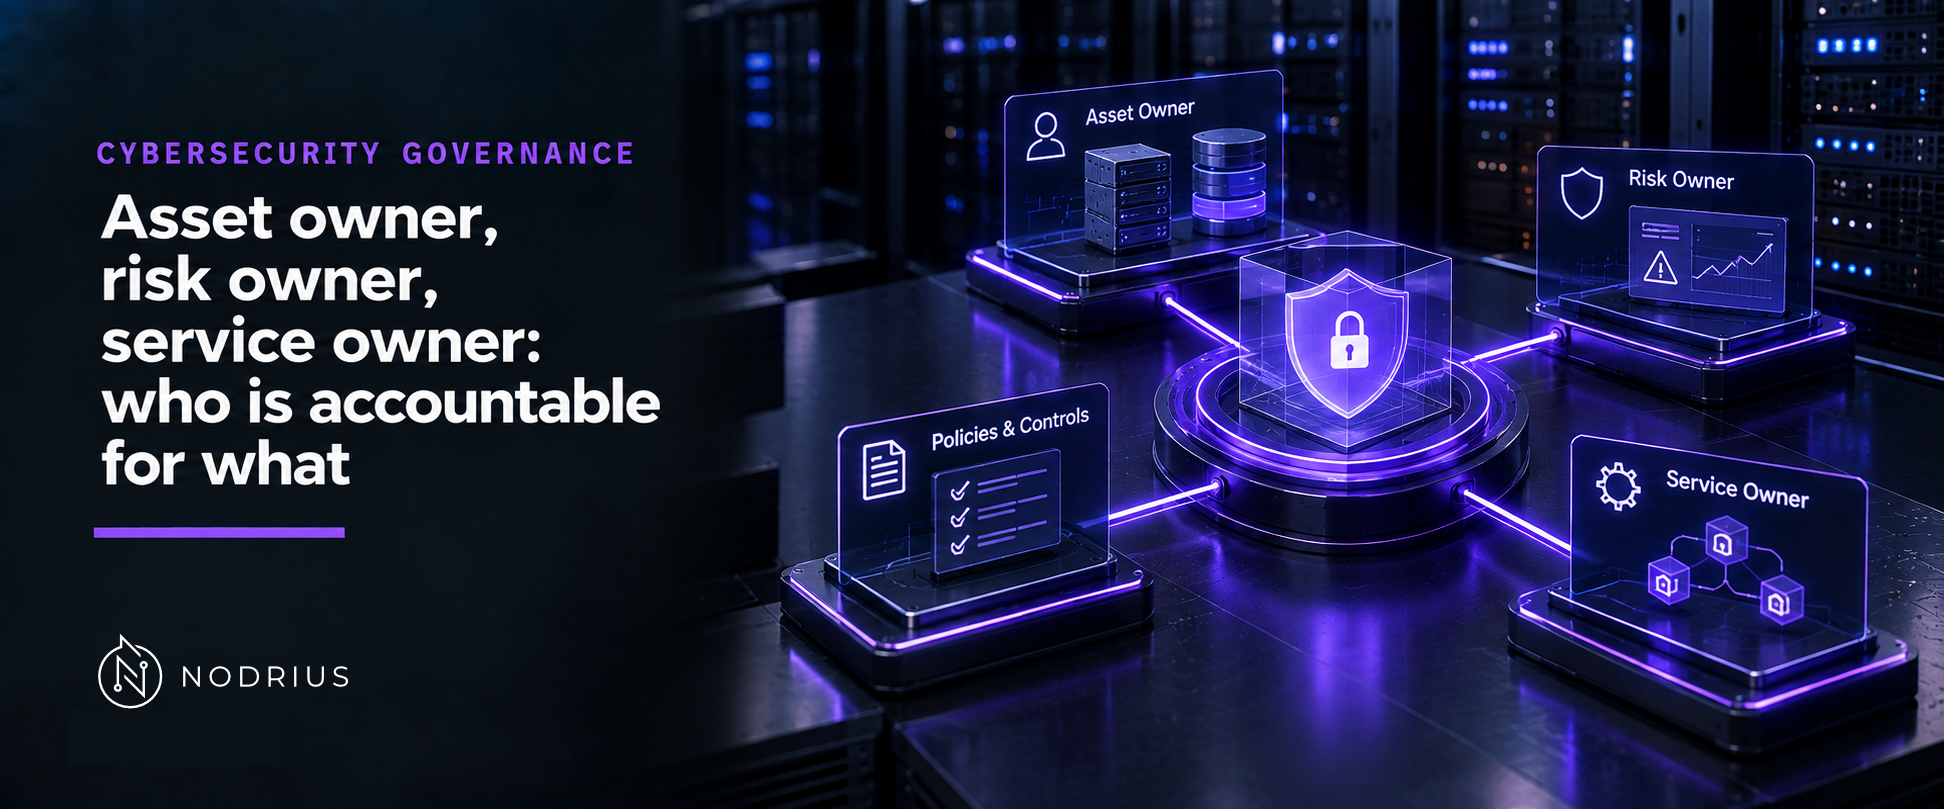
Asset, process and risk are owned differently; NIST names who is accountable for each.
An asset matters for its process and data; scope is a chain, not a perimeter.
Security protects three separate properties, not one attribute: each has its own impact.
Least privilege bounds one identity; defense in depth bounds one failure.
Policy states intent, standards bind, procedures give the steps, guidelines advise.